

Updated Oct-2026 Exam Engine or PDF for the SC-300 Tests Free Updated Today!
Ultimate Guide to Prepare SC-300 with Accurate PDF Questions
NEW QUESTION # 29
You have an Azure AD tenant that contains a user named User1 and a Microsoft 365 group named Group1. User1 is the owner of Group1.
You need to ensure that User1 is notified every three months to validate the guest membership of Group1.
What should you do?
- A. Configure an access package.
- B. Create an access review.
- C. Configure the External collaboration settings.
- D. Create a group expiration policy.
Answer: B
Explanation:
An access review is a process that allows you to review and manage the access of users and groups to resources. You can use access reviews to validate the guest membership of Group1 every three months.
NEW QUESTION # 30
You have an Azure subscription that contains the resource shown in the following table.
For which resources can you create an access review?
- A. Group1 only
- B. Group1, App1, Contributor, and Role1
- C. Hotel and Contributor only
- D. Group1, Role1, and Contributor only
Answer: A
NEW QUESTION # 31
You have a Microsoft 365 tenant and an Active Directory domain named adatum.com.
You deploy Azure AD Connect by using the Express Settings.
You need to configure self-service password reset (SSPR) to meet the following requirements:
When users reset their password, they must be prompted to respond to a mobile app notification or answer three predefined security questions.
Passwords must be synced between the tenant and the domain regardless of where the password was reset.
What should you do? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-sspr-deployment
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-authentication-security- questions
NEW QUESTION # 32
You have a Microsoft Entra tenant that contains two remote networks named RemoteNetworkl and RemoteNetwork2 and the users shown in the following table.
You have the devices shown in the following table.
Answer:
Explanation:
Explanation:
NEW QUESTION # 33
You need to meet the technical requirements for license management by the helpdesk administrators.
What should you create first, and which tool should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 34
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 E5 subscription.
You create a user named User1.
You need to ensure that User1 can update the status of Identity Secure Score improvement actions.
Solution: You assign the User Administrator role to User1.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
https://learn.microsoft.com/en-us/azure/active-directory/fundamentals/identity-secure-score#read- and-write-roles
NEW QUESTION # 35
You need to configure the assignment of Azure AD licenses to the Litware users. The solution must meet the licensing requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Litware recently added a custom user attribute named LWLicenses to the litware.com Active Directory forest.
Litware wants to manage the assignment of Azure AD licenses by modifying the value of the LWLicenses attribute. Users who have the appropriate value for LWLicenses must be added automatically to a Microsoft
365 group that has the appropriate licenses assigned.
NEW QUESTION # 36
You have an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.
For which users can you configure the Job title property and the Usage location property in Azure AD? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 37
You have an Azure subscription named Sub1 that contains two resource groups named RG1 and RG2. Sub1 contains the users shown in the following table.
Sub1 contains the resources shown in the following table.
You create the role-based access control (RBAC) role assignments shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation: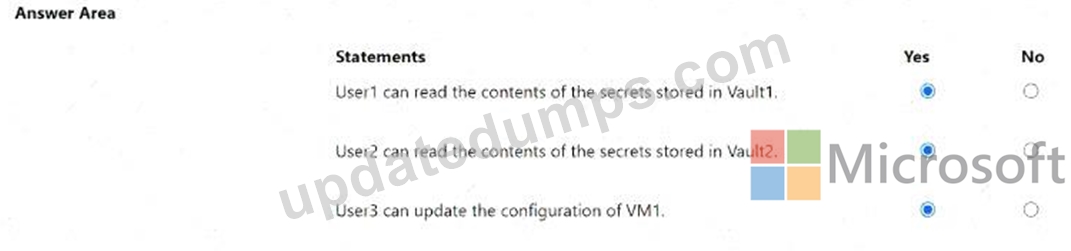
NEW QUESTION # 38
You have an on-premises datacenter that contains the hosts shown in the following table.
You have an Azure Active Directory (Azure AD) tenant that syncs to the Active Directory forest. Multi-factor authentication (MFA) is enforced for Azure AD.
You need to ensure that you can publish App1 to Azure AD users.
What should you configure on Server and Firewall1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/application-proxy
NEW QUESTION # 39
You have a Microsoft Entra tenant that contains the users shown in the following table: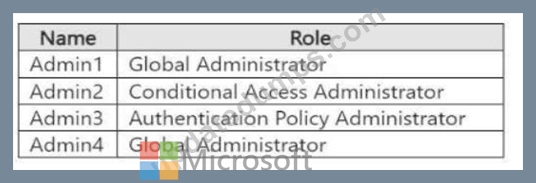
Admin4 creates a Conditional Access policy named Policy1 by using the "Require multifactor authentication for Azure management" template.
Which users will be required to use multi-factor authentication (MFA) the next time they sign in?
- A. Admin2 and Admin3 only
- B. Admin1 and Admin4 only
- C. Admin1, Admin2, and Admin3 only
- D. Admin1, Admin2, Admin3, and Admin4
Answer: B
Explanation:
Comprehensive and Detailed In-Depth
Let's break this down step by step based on Microsoft Entra ID Conditional Access policies, the "Require multifactor authentication for Azure management" template, and the roles assigned to the users, as outlined in Microsoft Identity and Access Administrator documentation.
Understanding the "Require multifactor authentication for Azure management" Template:
Microsoft Entra ID Conditional Access policies allow administrators to enforce security controls, such as requiring multi-factor authentication (MFA), based on specific conditions.
The "Require multifactor authentication for Azure management" template is a predefined Conditional Access policy template in Microsoft Entra ID. This template is designed to secure access to Azure management interfaces, such as the Azure portal, Azure PowerShell, Azure CLI, and other Azure management endpoints.
Key Details of the Template:
Cloud Apps or Actions:The template targets the "Microsoft Azure Management" cloud app. This includes all Azure management interfaces but does not apply to other cloud apps (e.g., Microsoft 365 apps).
Users:By default, the template applies to "All users," but it can be modified to include or exclude specific users or groups. The question does not specify any modifications, so we assume the default "All users" scope.
Conditions:Typically, there are no specific conditions (e.g., device state, location) in this template unless modified.
Grant Controls:The template enforces "Require multi-factor authentication" as the access control.
Therefore, this policy will require MFA for any user who attempts to access Azure management interfaces.
Understanding the Roles and Their Interaction with Azure Management:
Let's examine the roles assigned to each user and whether they are likely to interact with Azure management interfaces:
Admin1: Global Administrator
A Global Administrator has full access to all Microsoft Entra ID and Azure resources, including the ability to manage Azure subscriptions, resources, and the Azure portal.
Global Administrators frequently access Azure management interfaces (e.g., the Azure portal) to perform administrative tasks. Therefore, Admin1 will be subject to the Conditional Access policy when they sign in to access Azure management.
Admin2: Conditional Access Administrator
A Conditional Access Administrator can manage Conditional Access policies in Microsoft Entra ID but does not have direct access to Azure management interfaces by default.
This role is focused on Microsoft Entra ID, not Azure resource management. Unless Admin2 has been granted additional Azure roles (e.g., Contributor, Owner), they are unlikely to access Azure management interfaces. The question does not indicate any additional roles for Admin2, so we assume they do not interact with Azure management.
Admin3: Authentication Policy Administrator
An Authentication Policy Administrator can manage authentication methods and policies in Microsoft Entra ID (e.g., MFA settings, passwordless authentication).
Like the Conditional Access Administrator, this role is specific to Microsoft Entra ID and does not grant access to Azure management interfaces by default. Admin3 would not typically access Azure management unless assigned additional Azure roles, which are not specified.
Admin4: Global Administrator
Like Admin1, Admin4 is a Global Administrator and has full access to Azure management interfaces. Admin4 will be subject to the Conditional Access policy when accessing Azure management.
Applying the Conditional Access Policy:
The policy applies to "All users" (default scope of the template) and targets the "Microsoft Azure Management" cloud app.
The policy requires MFA for any user who accesses Azure management interfaces.
Admin1 and Admin4 (Global Administrators):
As Global Administrators, both Admin1 and Admin4 will access Azure management interfaces (e.g., the Azure portal) as part of their administrative duties.
The next time they sign in to access Azure management, the Conditional Access policy (Policy1) will enforce MFA.
Admin2 (Conditional Access Administrator) and Admin3 (Authentication Policy Administrator):
These roles do not inherently grant access to Azure management interfaces. Their responsibilities are limited to Microsoft Entra ID tasks, such as managing Conditional Access policies or authentication methods.
Unless Admin2 or Admin3 attempts to access Azure management (which they are not authorized to do by default), the policy will not apply to them. The question asks about the "next time they sign in," but the policy only triggers MFA when accessing the targeted cloud app (Microsoft Azure Management). If Admin2 and Admin3 sign in to Microsoft Entra ID or other apps (e.g., Microsoft 365), the policy does not apply.
Analysis of the Options:
A . Admin2 and Admin3 only:
Incorrect. Admin2 and Admin3 are not likely to access Azure management interfaces based on their roles, so the policy will not require MFA for them.
B . Admin1 and Admin4 only:
Correct. Admin1 and Admin4 are Global Administrators who will access Azure management interfaces, triggering the policy to require MFA the next time they sign in to those interfaces.
C . Admin1, Admin2, and Admin3 only:
Incorrect. Admin2 and Admin3 are not subject to the policy for the reasons stated above.
D . Admin1, Admin2, Admin3, and Admin4:
Incorrect. While the policy applies to "All users," only Admin1 and Admin4 (Global Administrators) are likely to access Azure management interfaces, triggering the MFA requirement.
Additional Considerations:
If Admin2 or Admin3 were assigned additional Azure roles (e.g., Contributor, Owner) that grant access to Azure management, they would also be subject to the policy. However, the question does not indicate any such roles.
The phrase "the next time they sign in" can be misleading. The policy only enforces MFA when the user signs in to the targeted cloud app (Microsoft Azure Management). IfAdmin2 or Admin3 signs in to a different app (e.g., Microsoft 365), the policy does not apply.
If the policy were modified to target a different cloud app (e.g., "All apps") or to include specific users, the answer might change. However, the question specifies the default template behavior.
Conclusion:The Conditional Access policy (Policy1) created using the "Require multifactor authentication for Azure management" template will require MFA for users who access Azure management interfaces. Based on their roles:
Admin1 and Admin4 (Global Administrators) will be required to use MFA the next time they sign in to Azure management.
Admin2 and Admin3 (Conditional Access Administrator and Authentication Policy Administrator) are not likely to access Azure management, so the policy does not apply to them.Therefore, the correct answer isB.
Reference:
Microsoft Entra ID Conditional Access documentation: "Common Conditional Access policies - Require MFA for Azure management" (Microsoft Learn:https://learn.microsoft.com/en-us/entra/identity/conditional-access/concept-conditional-access-policy-common#require-mfa-for-azure-management) Microsoft Entra ID role documentation: "Administrator role permissions in Microsoft Entra ID" (Microsoft Learn:https://learn.microsoft.com/en-us/entra/identity/role-based-access-control/permissions-reference) Microsoft Identity and Access Administrator (SC-300) exam study guide, which covers Conditional Access policies and their application to specific roles and cloud apps.
NEW QUESTION # 40
You have a Microsoft Entra tenant that contains the users shown in the following table:
Admin4 creates a Conditional Access policy named Policy1 by using the "Require multifactor authentication for Azure management" template.
Which users will be required to use multi-factor authentication (MFA) the next time they sign in?
- A. Admin2 and Admin3 only
- B. Admin1, Admin2, and Admin3 only
- C. Admin1 and Admin4 only
- D. Admin1, Admin2, Admin3, and Admin4
Answer: B
NEW QUESTION # 41
Case Study 1 - Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and branch offices in London and Seattle.
Contoso has a partnership with a company named Fabrikam, Inc. Fabrikam has an Azure Active Directory (Azure AD) tenant named fabrikam.com.
Existing Environment. Existing Environment
The on-premises network of Contoso contains an Active Directory domain named contoso.com.
The domain contains an organizational unit (OU) named Contoso_Resources. The Contoso_Resources OU contains all users and computers.
The contoso.com Active Directory domain contains the users shown in the following table.
Existing Environment. Microsoft 365/Azure Environment
Contoso has an Azure AD tenant named contoso.com that has the following associated licenses:
* Microsoft Office 365 Enterprise E5
* Enterprise Mobility + Security
* Windows 10 Enterprise E3
* Project Plan 3
Azure AD Connect is configured between Azure AD and Active Directory Domain Services (AD DS). Only the Contoso_Resources OU is synced.
Helpdesk administrators routinely use the Microsoft 365 admin center to manage user settings.
User administrators currently use the Microsoft 365 admin center to manually assign licenses. All users have all licenses assigned besides the following exceptions:
* The users in the London office have the Microsoft 365 Phone System license unassigned.
* The users in the Seattle office have the Yammer Enterprise license unassigned.
Security defaults are disabled for contoso.com.
Contoso uses Azure AD Privileged Identity Management (PIM) to protect administrative roles.
Existing Environment. Problem Statements
Contoso identifies the following issues:
* Currently, all the helpdesk administrators can manage user licenses throughout the entire Microsoft 365 tenant.
* The user administrators report that it is tedious to manually configure the different license requirements for each Contoso office.
* The helpdesk administrators spend too much time provisioning internal and guest access to the required Microsoft 365 services and apps.
* Currently, the helpdesk administrators can perform tasks by using the User administrator role without justification or approval.
* When the Logs node is selected in Azure AD, an error message appears stating that Log Analytics integration is not enabled.
Requirements. Planned Changes
Contoso plans to implement the following changes:
* Implement self-service password reset (SSPR).
* Analyze Azure audit activity logs by using Azure Monitor.
* Simplify license allocation for new users added to the tenant.
* Collaborate with the users at Fabrikam on a joint marketing campaign.
* Configure the User administrator role to require justification and approval to activate.
* Implement a custom line-of-business Azure web app named App1. App1 will be accessible from the internet and authenticated by using Azure AD accounts.
* For new users in the marketing department, implement an automated approval workflow to provide access to a Microsoft SharePoint Online site, group, and app.
Contoso plans to acquire a company named Adatum Corporation. One hundred new ADatum users will be created in an Active Directory OU named Adatum. The users will be located in London and Seattle.
Requirement. Technical Requirements
Contoso identifies the following technical requirements:
* All users must be synced from AD DS to the contoso.com Azure AD tenant.
* App1 must have a redirect URI pointed to https://contoso.com/auth- response.
* License allocation for new users must be assigned automatically based on the location of the user.
* Fabrikam users must have access to the marketing department's SharePoint site for a maximum of 90 days.
* Administrative actions performed in Azure AD must be audited. Audit logs must be retained for one year.
* The helpdesk administrators must be able to manage licenses for only the users in their respective office.
* Users must be forced to change their password if there is a probability that the users' identity was compromised.
Hotspot Question
You need to implement the planned changes and technical requirements for the marketing department.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management- organization
NEW QUESTION # 42
You have an Azure Active Directory (Azure AD) tenant named contoso.com.
All users who run applications registered in Azure AD are subject to conditional access policies.
You need to prevent the users from using legacy authentication.
What should you include in the conditional access policies to filter out legacy authentication attempts?
- A. a cloud apps or actions condition
- B. a sign-in risk condition
- C. a client apps condition
- D. a user risk condition
Answer: C
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/block-legacy-authentication
NEW QUESTION # 43
You need to meet the authentication requirements for leaked credentials.
What should you do?
- A. Enable password hash synchronization in Azure AD Connect.
- B. Configure Azure AD Password Protection.
- C. Enable federation with PingFederate in Azure AD Connect.
- D. Configure an authentication method policy in Azure AD.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security/fundamentals/steps-secure-identity
Topic 1, Litware, Inc
Identity Environment
The network contains an Active Directory forest named litware.com that is linked to an Azure Active Directory (Azure AD) tenant named litware.com. Azure AD Connect uses pass-through authentication and has password hash synchronization disabled.
Litware.com contains a user named User1 who oversees all application development. Litware implements Azure AD Application Proxy.
Fabrikam has an Azure AD tenant named fabrikam.com. The users at Fabrikam access the resources in litware.com by using guest accounts in the litware.com tenant.
Cloud Environment
All the users at Litware have Microsoft 365 Enterprise E5 licenses. All the built-in anomaly detection polices in Microsoft Cloud App Security are enabled.
Litware has an Azure subscription associated to the litware.com Azure AD tenant. The subscription contains an Azure Sentinel instance that uses the Azure Active Directory connector and the Office 365 connector. Azure Sentinel currently collects the Azure AD sign-ins logs and audit logs.
On-premises Environment
The on-premises network contains the severs shown in the following table.
Both Litware offices connect directly to the internet. Both offices connect to virtual networks in the Azure subscription by using a site-to-site VPN connection. All on-premises domain controllers are prevented from accessing the internet.
Delegation Requirements
Litware identifies the following delegation requirements:
* Delegate the management of privileged roles by using Azure AD Privileged Identity Management (PIM).
* Prevent nonprivileged users from registering applications in the litware.com Azure AD tenant-
* Use custom catalogs and custom programs for Identity Governance.
* Ensure that User1 can create enterprise applications in Azure AD. Use the principle of least privilege.
Licensing Requirements
Litware recently added a custom user attribute named LWLicenses to the litware.com Active Directory forest. Litware wants to manage the assignment of Azure AD licenses by modifying the value of the LWLicenses attribute. Users who have the appropriate value for LWLicenses must be added automatically to Microsoft 365 group that he appropriate license assigned.
Management Requirement
Litware wants to create a group named LWGroup1 will contain all the Azure AD user accounts for Litware but exclude all the Azure AD guest accounts.
Authentication Requirements
Litware identifies the following authentication requirements:
* Implement multi-factor authentication (MFA) for all Litware users.
* Exempt users from using MFA to authenticate to Azure AD from the Boston office of Litware.
* Implement a banned password list for the litware.com forest.
* Enforce MFA when accessing on-premises applications.
* Automatically detect and remediate externally leaked credentials
Access Requirements
Litware wants to create a group named LWGroup1 that will contain all the Azure AD user accounts for Litware but exclude all the Azure AD guest accounts.
Monitoring Requirements
Litware wants to use the Fusion rule in Azure Sentinel to detect multi-staged that include a combination of suspicious Azure AD sign-ins followed by anomalous Microsoft Office 365 activity.
NEW QUESTION # 44
You have a Microsoft Entra tenant that contains a group named Group1 and two users named User1 and User2. User1 is a member of Group1.
You register an enterprise application named App1.
You enable self-service application access for App1 and configure the following settings:
Allow users to request access to this application: Yes
To which group should assigned users be added: Group1
Require approval before granting access to this application: Yes
Who is allowed to approve access to this application: User2
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Answer:
Explanation:
Explanation:
User1 must request access to App1 before they can use the app: No
If User2 requests access to App1, they will be added to Group1 automatically: Yes User2 can approve App1 requests by using the Microsoft Entra admin center: Yes Let's break this down step by step based on Microsoft Entra ID self-service application access and the configured settings, as outlined in Microsoft Identity and Access Administrator documentation.
Understanding Self-Service Application Access in Microsoft Entra ID:
Self-service application access in Microsoft Entra ID allows users to request access to applications without needing an administrator to manually assign them. This is configured on a per-application basis.
The settings for App1 are:
Allow users to request access to this application: Yes- Users can request access to App1.
To which group should assigned users be added: Group1- Users who are granted access will be added to Group1, which provides the necessary permissions to use App1.
Require approval before granting access to this application: Yes- Access requests must be approved before the user is added to Group1.
Who is allowed to approve access to this application: User2- User2 is the designated approver for access requests to App1.
Statement 1: User1 must request access to App1 before they can use the app.
Analysis:
User1 is already a member of Group1, as stated in the question.
The self-service settings specify that users who are granted access to App1 will be added to Group1. This implies that membership in Group1 is what grants access to App1.
Since User1 is already a member of Group1, they already have access to App1. In Microsoft Entra ID, if a user is already assigned to an application (either directly or via group membership), they do not need to request access through the self-service process-they can simply use the app.
The self-service access request process is for users who are not yet assigned to the app (i.e., not in Group1).
Since User1 is already in Group1, they do not need to request access.
Conclusion:This statement isNo. User1 does not need to request access because they are already a member of Group1 and can use App1 immediately.
Statement 2: If User2 requests access to App1, they will be added to Group1 automatically.
Analysis:
User2 is not a member of Group1 (the question does not state that User2 is in Group1).
The self-service settings allow users to request access to App1, and the setting "To which group should assigned users be added: Group1" means that users who are granted access will be added to Group1.
However, the setting "Require approval before granting access to this application: Yes" means that User2's request must be approved before they are added to Group1. The approver for App1 requests is User2 themselves, which introduces a potential conflict.
In Microsoft Entra ID, if a user is both the requester and the approver, the system typicallyallows them to approve their own request (unless additional policies prevent this, which is not specified in the question).
Therefore, User2 can request access and approve their own request.
Once the request is approved, User2 will be added to Group1 automatically as per the self-service settings.
The term "automatically" in the statement refers to the process after approval-once approved, the addition to Group1 happens without further manual intervention.
Conclusion:This statement isYes. If User2 requests access to App1 and approves their own request, they will be added to Group1 automatically.
Statement 3: User2 can approve App1 requests by using the Microsoft Entra admin center.
Analysis:
The self-service settings specify that User2 is the designated approver for access requests to App1.
In Microsoft Entra ID, approvers can manage access requests through the Microsoft Entra admin center (via the "My Access" portal or the "Access Requests" section, depending on their role and permissions).
User2, as the designated approver, will receive a notification (via email or the My Access portal) when a request is made. They can then log into the Microsoft Entra admin center, navigate to the access requests section, and approve or deny the request.
Even though User2 is not explicitly an admin, the fact that they are designated as the approver for App1 requests grants them the ability to approve requests through the Microsoft Entra admin center.
Conclusion:This statement isYes. User2 can approve App1 requests using the Microsoft Entra admin center.
Additional Considerations:
If User2 were not allowed to approve their own request (e.g., due to a separation of duties policy), Statement
2 might be affected. However, Microsoft Entra ID does not enforce such a restriction by default, and the question does not specify any additional policies.
The Microsoft Entra admin center is the primary interface for managing access requests, but users can also approve requests via email links or the My Access portal. The statement specifically mentions the admin center, which is a valid method.
Conclusion:
Statement 1:No- User1 does not need to request access since they are already in Group1.
Statement 2:Yes- User2 will be added to Group1 automatically after their request is approved (by themselves).
Statement 3:Yes- User2 can approve requests using the Microsoft Entra admin center.
References:
Microsoft Entra ID documentation: "Configure self-service application access" (Microsoft Learn:https://learn.
microsoft.com/en-us/entra/identity/enterprise-apps/configure-self-service) Microsoft Entra ID documentation: "Manage access requests" (Microsoft Learn:https://learn.microsoft.com
/en-us/entra/identity/governance/access-reviews-overview)
Microsoft Identity and Access Administrator (SC-300) exam study guide, which covers self-service application access and approval workflows in Microsoft Entra ID.
NEW QUESTION # 45
You have an Azure subscription that contains a virtual machine named VM1. VM1 has the following configurations:
* Private IP address: 172.16.1.5
* Public IP address 10fl.143.16U5
* System-assigned managed identity status: On
You install an app named App1 on VM1.
You need to configure App1 to request a managed identity app-only access token. Which IP address should App1 use for the request?
- A. 108.143.161.25
- B. 169.254.169.254
- C. 127.0.0.1
- D. 172.1615
Answer: B
NEW QUESTION # 46
You have an Azure Active Directory (Azure AD) tenant that has multi-factor authentication (MFA) enabled.
The account lockout settings are configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 47
You have a Microsoft 365 E5 subscription.
You have an Azure subscription that is linked to a Microsoft Entra tenant. The tenant contains a user named User1.
You plan to deploy Microsoft Entra Permissions Management.
You need to ensure that User1 can onboard the Azure subscription to Permissions Management. The solution must follow the principle of least privilege.
Which Microsoft Entra role should you assign to User1?
- A. Permissions Management Administrator
- B. Global Administrator
- C. Application Administrator
- D. Security Administrator
Answer: A
Explanation:
In Microsoft Entra Permissions Management (formerly CloudKnox), the Permissions Management Administrator role provides the least-privilege rights necessary to onboard cloud environments such as Azure subscriptions, AWS accounts, or GCP projects. This role allows users to configure data collection and onboard environments without granting global administrative access.
The Global Administrator role could also perform onboarding but exceeds the least-privilege requirement.
Microsoft's official documentation (SC-300 "Manage Microsoft Entra Permissions Management" module) clearly states:
"The Permissions Management Administrator can onboard and configure environments for Permissions Management and manage discovery and insights across multi-cloud platforms."
NEW QUESTION # 48
You have a Microsoft 365 tenant
You currently allow email clients that use Basic authentication to connect to Microsoft Exchange Online.
You need to ensure that users can connect to Exchange Online only from email clients that use Modern authentication protocols.
What should you implement?
- A. a Microsoft Intune compliance policy
- B. a Microsoft Defender for Cloud Apps OAuth policy
- C. a Microsoft Intune app protection policy
- D. a Microsoft Entra conditional access policy
Answer: D
NEW QUESTION # 49
You have a Microsoft 365 E5 subscription and an Azure subscription. You need to meet the following requirements:
* Ensure that users can sign in to Azure virtual machines by using their Microsoft 365 credentials.
* Delegate the ability to create new virtual machines.
What should you use for each requirement? To answer, drag the appropriate features to the correct requirements. Each feature may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
Answer:
Explanation: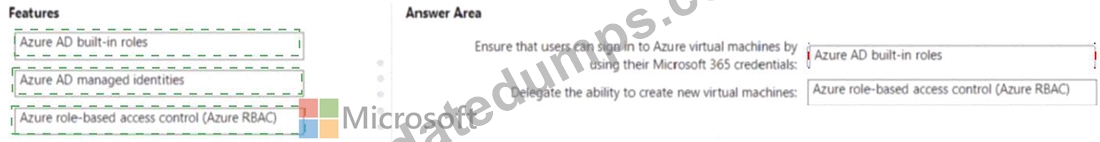
Explanation:
NEW QUESTION # 50
......
The Microsoft SC-300 exam covers a wide range of topics, including identity and access management (IAM) concepts, Azure Active Directory (Azure AD) management, authentication and authorization mechanisms, conditional access policies, identity protection, and privileged identity management (PIM). It also includes hands-on experience with Azure AD Connect, Azure AD Identity Protection, Azure AD Privileged Identity Management, and other related tools and services.
Pass Microsoft With UpdateDumps Exam Dumps: https://www.updatedumps.com/Microsoft/SC-300-updated-exam-dumps.html
Fully Updated SC-300 Dumps - 100% Same Q&A In Your Real Exam: https://drive.google.com/open?id=10nKq1o6ac3u3PymJHTEfNYQfup2gmSbH